You vibe-coded it. Now make it hold up.
Lovable, Bolt, Cursor and Replit get an app to a demo fast. Real users, real data and real payments are a different test. We review what the AI wrote, close the holes, clean up what will not scale, and keep it running, without throwing away what works.
Sound familiar?
- Every new prompt fixes one thing and breaks two others.
- Users might be able to see or change data that is not theirs, and nobody can say for sure.
- API keys and secrets live in the frontend code or somewhere in the repository.
- It works on the demo account and falls over when real users arrive.
- Payments, emails or webhooks fail quietly, and you hear about it from a customer.
- Nobody on the team can explain what the code actually does.
Who this is for, and who it is not.
A good fit if
- You have a working prototype or early product, real users are coming, and you want to keep it rather than start over.
- It was built with Lovable, Bolt, v0, Replit, Cursor, Claude Code or similar, on something like React or Next.js with Supabase, Firebase or Node.
- You need someone accountable for security, data and uptime from here on.
Probably not the right call if
- You are still validating the idea and nobody uses it yet. Keep prompting; it is cheaper.
- You want a rewrite on day one. Sometimes that is right, but we decide it after reading the code, not before.
- You want someone to keep prompting the same tool for you.
The vibe-coded app security checklist
Sixteen checks we run on every AI-built app before it meets real users. Tick what you can confirm today; the list stays in your browser.
0 of 16 confirmed
Tick only what you can confirm, not what you assume. Several basics are unconfirmed. That is normal for an AI-built app, and it is exactly what the review covers. In good shape. The unticked items are where incidents usually start. All sixteen confirmed. Keep it that way as the app changes.
Access and data
Secrets and keys
Input and abuse
Payments and integrations
Running it
Not sure about some of these? We check all sixteen on your real code and infrastructure in the system review, and fix the dangerous ones first.
Book a System ReviewHow it works.
-
01
System review, in about a week
We read the code, the database rules, the hosting and the integrations, run the checklist above for real, and write down what is broken, what is fragile and what is fine. Fixed price, and the report is yours to keep.
-
02
Fix the dangerous things first
Exposed data, leaked keys, missing server-side checks and unverified payments come before anything cosmetic. This part is usually days, not weeks.
-
03
Clean up what will not scale
Logic moves out of the frontend, tests go around the parts that earn money, and staging, backups, logging and alerts are set up. The code lives in a repository you own.
-
04
Keep it running
On a monthly plan the same engineers patch, monitor and keep shipping. You can still prompt your own prototypes; we make sure what reaches production is safe.
We build with the same tools, in production.
Our own products are written with AI coding agents every day and run with real users and payments. We know where AI-written code breaks because we fix it in our own. We also take over systems in a bad state and make them safe.
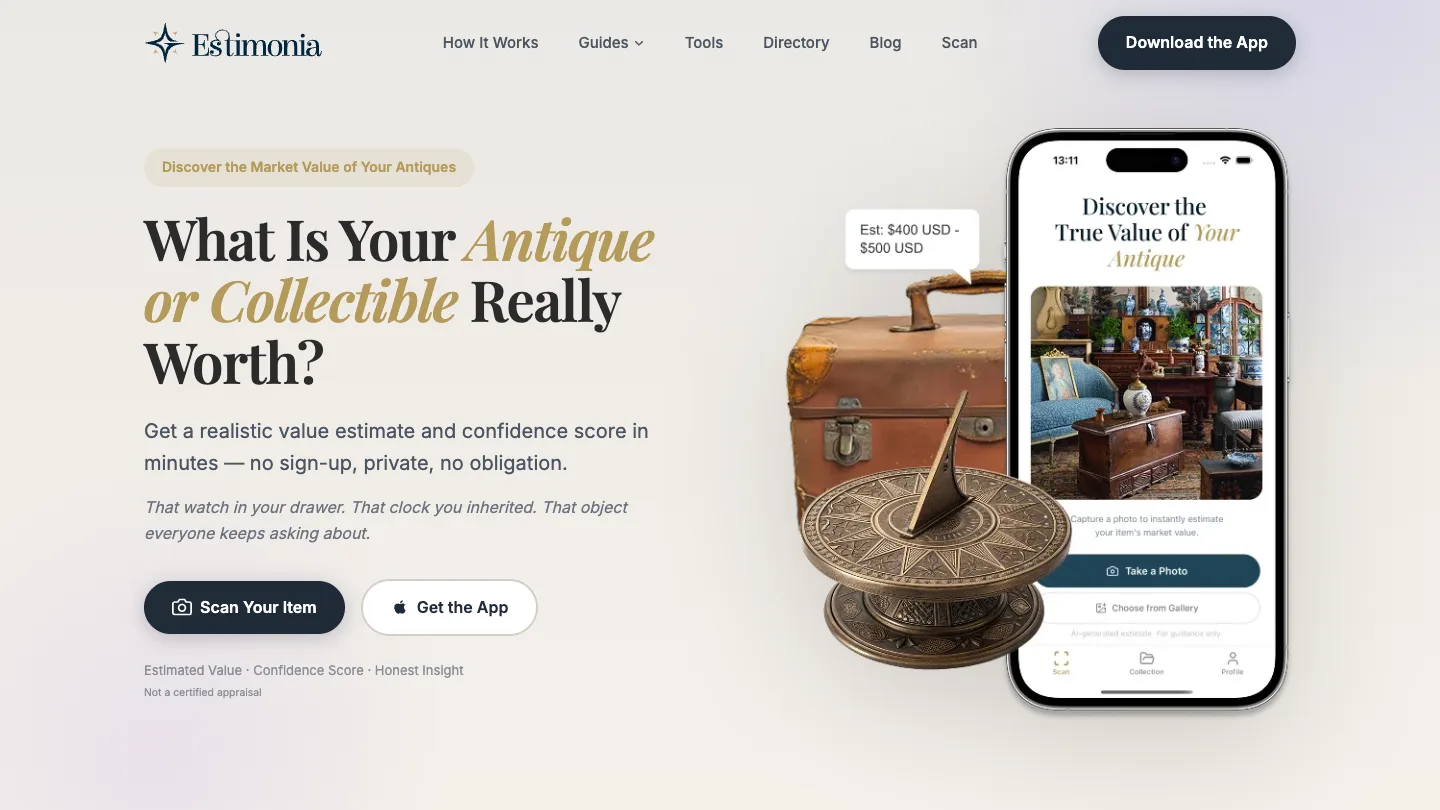
Estimonia
LiveEstimonia: AI Photo Valuation for Antiques, on Web and iOS
Estimonia is our own product. Upload photos of an antique, watch or piece of jewellery and get a USD value range, a confidence score and a written rationale. We built and run it end to end: a Laravel 12 API with queued vision analysis, a web scanner, an Expo iOS app and an auction house directory.
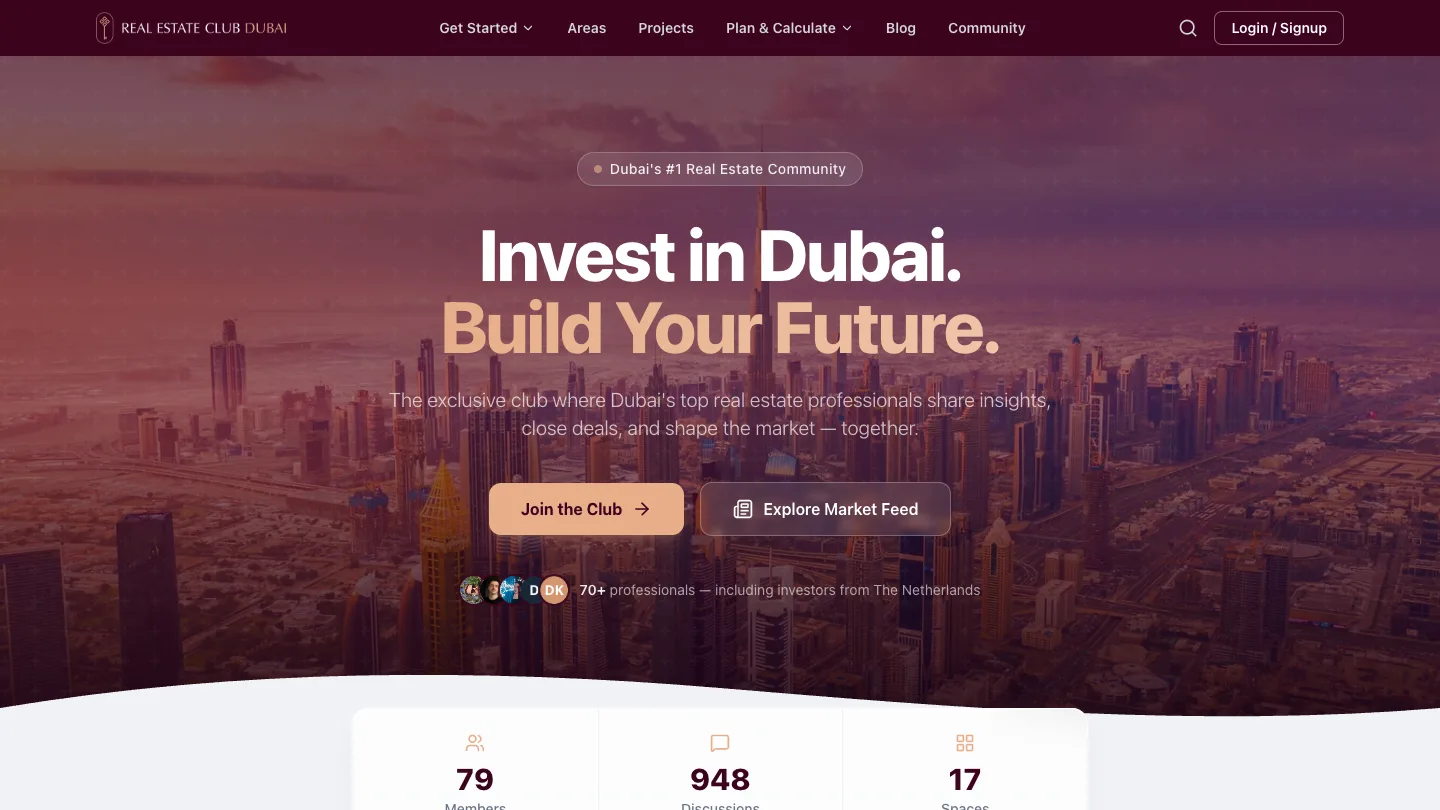
Real Estate Club Dubai
LiveReal Estate Club Dubai: a data-grounded property platform and iOS app
Our own product. We built a Dubai property platform on Laravel: a 24-category service directory, published ranking methodology, calculators, a handover tracker synced from the Dubai Land Department registry, a tool-calling AI advisor grounded in our database, and a native iOS app on the same API.
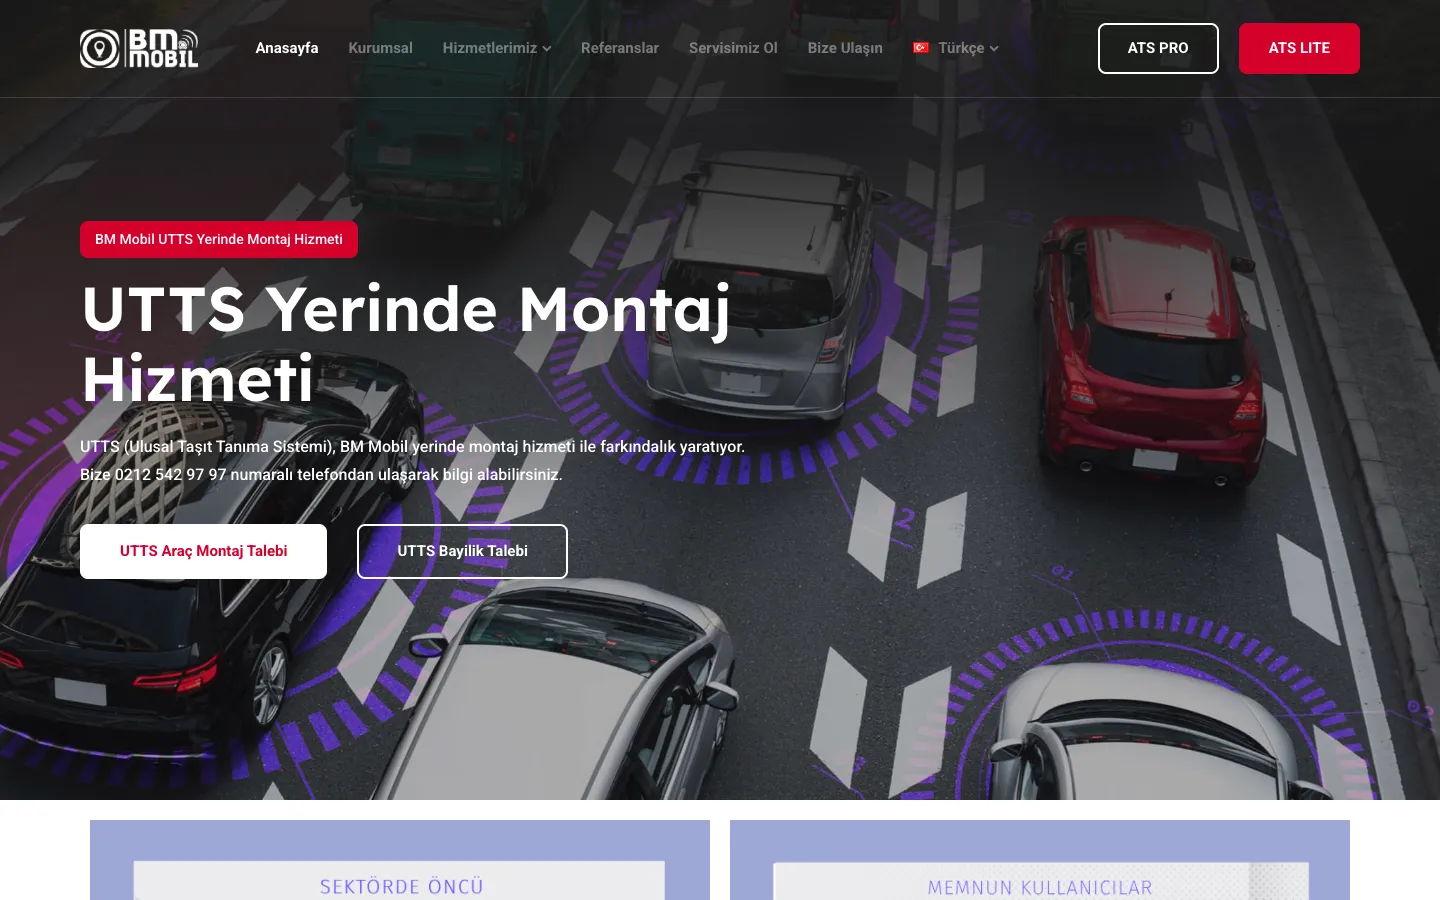
BM Mobil
LiveBM Mobil: Taking Over and Hardening a Corporate WordPress Site
We took over a corporate WordPress site after a security incident: regained control safely, audited it for backdoors, closed the common entry points and handed the business a ranked upgrade plan.
Published prices, fixed before we start.
€1,000
delivered within a week
We read the system you already have and tell you what is actually wrong with it, what it would take to fix, and what it would cost.
€5,000 – €20,000
typical project
Fixed scope, fixed price, agreed before anyone writes code. Most of what we do sits in this band.
from €750
per month
We take the system over and keep it alive. This is the part most people discover they needed about six months after launch.
Most rescues start with the €1,000 system review. It comes off the fix in full if you go ahead within 30 days, and it tells you honestly if a rewrite would be cheaper.
Full pricing and termsQuestions we get asked.
Rarely. Most vibe-coded apps have a sound shape and a few dangerous gaps. We keep what works and replace what cannot be made safe. If a rewrite would genuinely be cheaper, the review says so, with the numbers.
Apps built with Lovable, Bolt, v0, Replit, Cursor and Claude Code, typically React or Next.js on Supabase, Firebase, Node or Python. When a product has outgrown its first stack, we also move it onto Laravel.
Yes, and you should. We set up a staging environment and a review step so prompts can keep producing features without shipping a security hole straight to production.
Usually within a week. The system review itself takes about five working days, and critical issues are reported the day we find them, not at the end.
If you need one, yes. Either way, access is read-only for the review, and we work in your repository and your accounts from the first day.